Resolved: all websites are back online
The security update for PHP has been installed on all our servers, and we have checked on each server to ensure that the websites are working properly. Since the early morning of October 22nd, all websites have been back online.
No hack has taken place on our servers., and we have found no indications of abuse.
What was going on
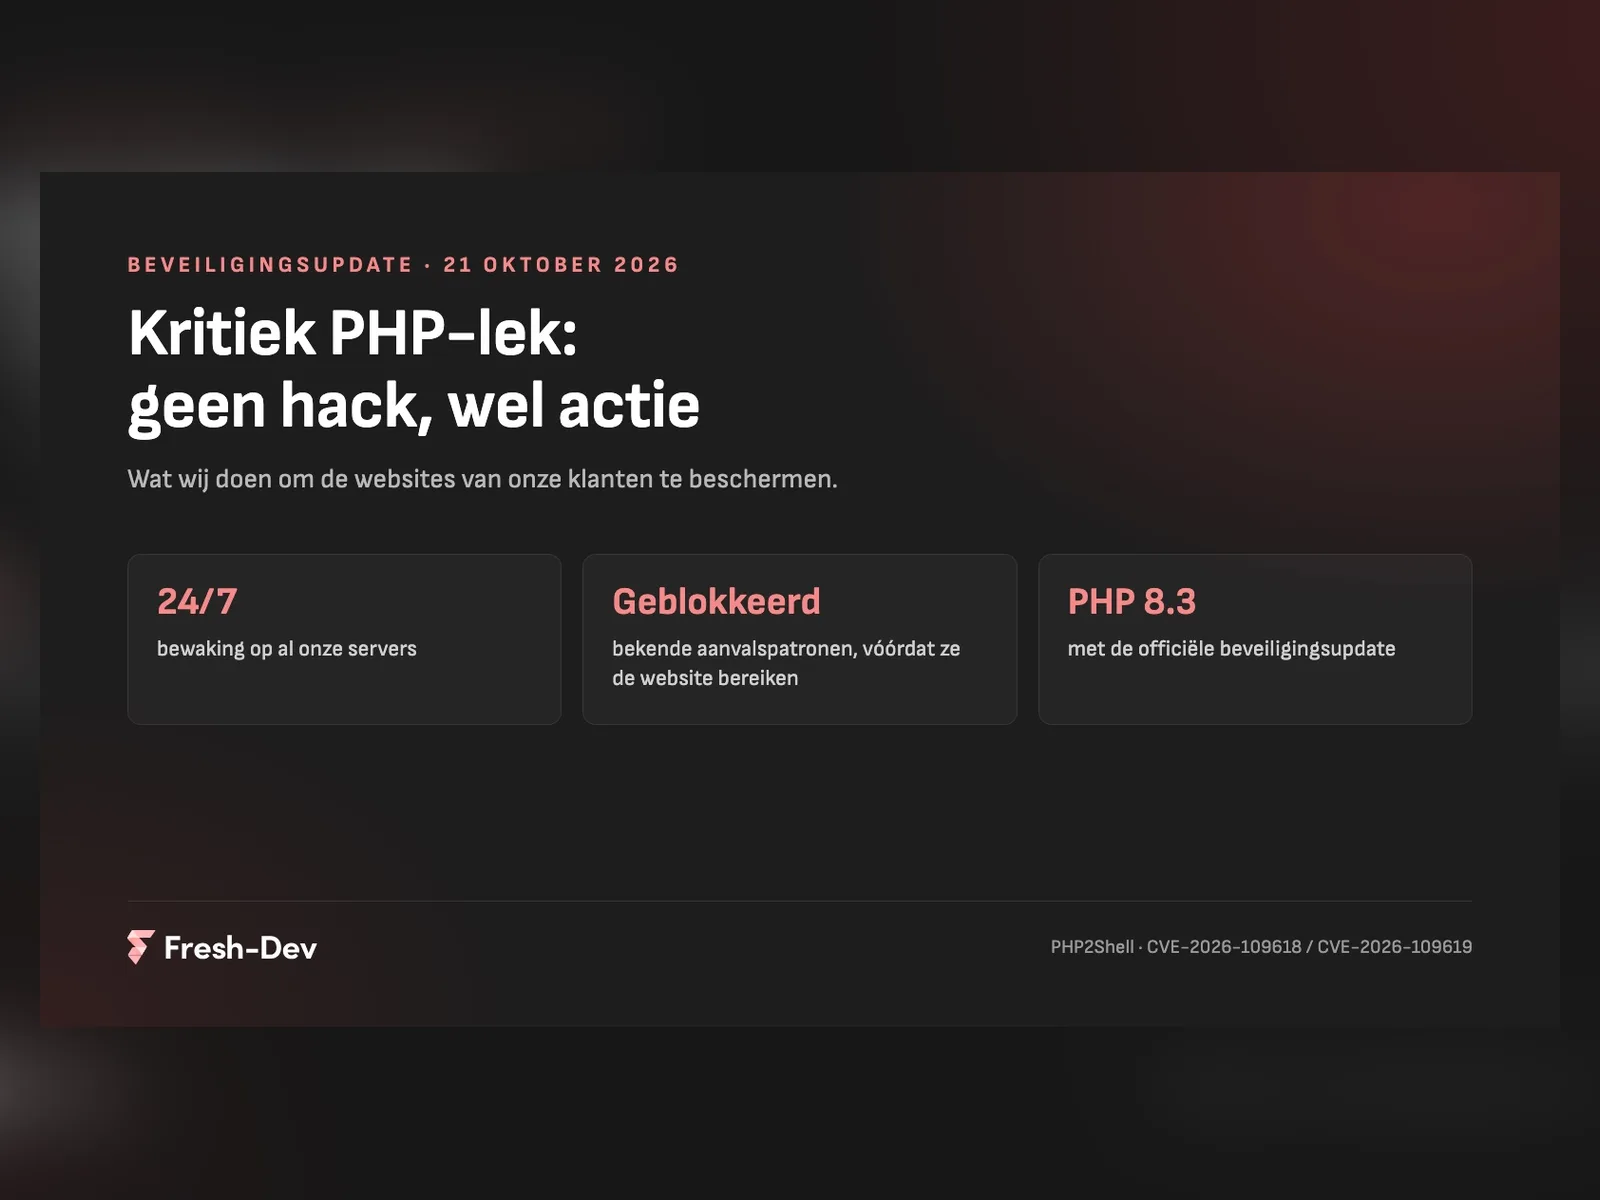
PHP is the programming language on which, among other things, WordPress runs. Globally, about 70 percent of all websites use PHP. Researchers found two serious vulnerabilities (CVE-2026-109618 and CVE-2026-109619). This allowed someone to execute code remotely on a web server, without logging in.
Normally, such an update goes smoothly: the PHP team fixes the problem, shares it in advance with the server software vendors, and at a scheduled time everything comes out at the same time. This time that didn’t happen. One of the discoverers published a video with details too early, and another company released the repaired version six hours before the scheduled time. As a result, the information was already public while most vendors had not yet finished their updates. Organizations around the world took precautions by taking their websites offline, including DigiD, the Tweede Kamer, and Tweakers.
Why we went offline, and why it lasted into the night
On October 21st, we first did everything to keep the websites online safely: extra monitoring, blocking of the known attack patterns, and migrating websites to a newer PHP version. When it became clear how great the risk was, we decided to temporarily take the servers offline.
PHP released the update at 16:00. Our servers are running on CloudLinux, an operating system specifically designed for web servers that run many websites side by side. CloudLinux provides its own PHP versions, and those had to process the update first. At 21:00, CloudLinux reported that the update was ready, but later that evening it turned out that it was not yet valid for the version our servers were using. The correct packages only became available after midnight. We deliberately waited until everything was updated, rather than going online with a half-baked solution earlier.
What we continue to do
In the coming days, we will continue to maintain the additional surveillance and security measures. With such a large leak, there may be further updates that we will install immediately.
You can always track the status of our services at status.fresh-dev.nl. On that page, we will also post updates about outages and maintenance from now on.
Do you have to do something yourself?
No. If something doesn't work the way you're used to, please let us know via info@fresh-dev.nl, Then we’ll look into it immediately.